Strategic Advisory
Security strategy, operating models, board-level reporting and CISO support for organisations strengthening or transforming their security program.
Read more
From executive strategy to technical execution, we help organisations assess, secure and strengthen their digital assets. Senior expertise across advisory, application and AI security, engineering and offensive testing — focused on practical outcomes.
Most organisations do not lack security findings. They lack a clear line between a risk, the decision it demands, and the control that closes it.
Eshay Advisory sits on both sides of that line. We advise executive committees on governance and exposure, and we work with engineering teams to design, test and secure what actually gets deployed — from applications and cloud platforms to AI agents, identities and automation.
Read our methodology
Eight complementary capabilities, delivered by senior specialists — keeping strategy, engineering and security testing closely aligned.
Security strategy, operating models, board-level reporting and CISO support for organisations strengthening or transforming their security program.
Read morePosture assessment against ISO 27001, GDPR, NIS2 and sector regulation. Gaps identified, risks prioritised, governance strengthened.
Read moreSecure architecture, threat modelling, design reviews, code and pipeline assessment — from identifying weaknesses to implementing effective controls with engineering teams.
Read moreTargeted and full-scope testing that uncovers real attack paths, exploitable weaknesses and business-impacting weaknesses.
Read moreConfiguration and permission model review, access control analysis, secure integration design and governance.
Read moreDark web monitoring for credential leaks and exposed assets, plus curated contextual intelligence that SOC teams can actually act on.
Read moreHands-on DevSec Champions programs for developers and engineers, built on secure coding and real attack scenarios — not slideware.
Read moreSecurity for AI systems and autonomous agents — covering identities, permissions, secrets, data access, tool execution and the actions they can perform.
Read moreAI security is not only about the model. Agentic systems can hold credentials, access sensitive data, call tools and trigger actions across systems that were never designed for autonomous use.
We assess AI applications, autonomous agents and the automation around them — mapping identities, permissions, secrets, data access and tool execution, then testing how those controls behave under hostile input.
Explore AI & Agentic Security
The architecture on the screen and the risk on the board agenda are the same conversation. We are the firm that can hold both.
Purpose-built platforms supporting training, exposure monitoring and security governance — available standalone or alongside our services.
A structured program that turns selected developers into security referents inside their own squads — hands-on labs, real attack scenarios and measurable progression.
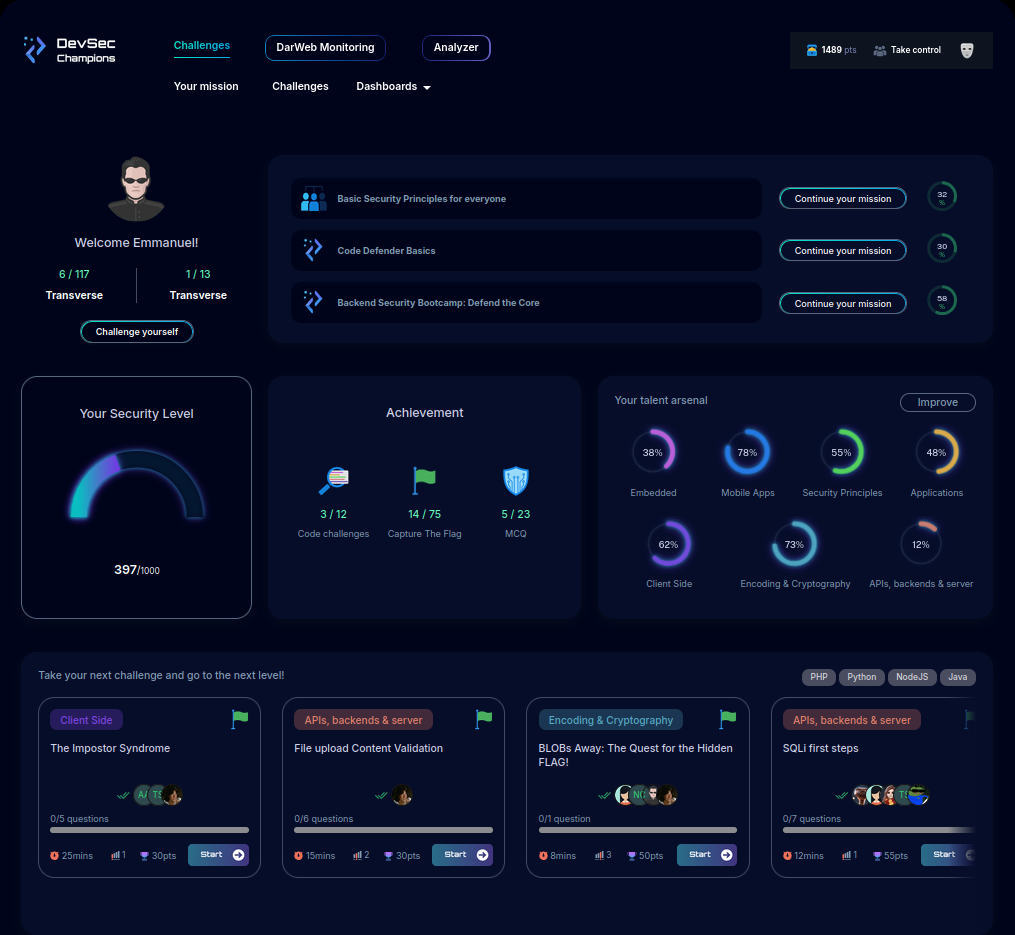
Most breaches don't start with sophisticated exploits—they start with exposed credentials or secrets. We continuously monitor the dark web, public repositories and external sources to detect leaked credentials, API keys, tokens and other sensitive information before attackers can use them.
Guardrails for Salesforce and agentic AI deployments: permission drift detection, data-exposure analysis and policy enforcement for autonomous agents operating on customer data.

A consistent approach, scaled to the environment — from focused assessments to ongoing security programs.
Assets, dependencies, controls and regulatory obligations mapped against credible threat scenarios — not a generic questionnaire.
Findings translated into a prioritised, costed decision set, then engineered into place with your teams and your constraints.
Continuous exposure monitoring, threat intelligence and control verification, so posture does not quietly decay after the report.
Controls are refined, automated and integrated into day-to-day operations so improvements remain effective beyond the engagement.
Exposed credentials, leaked secrets and publicly accessible sensitive information are often discovered by attackers long before organisations become aware of them.
Eshay Sentinel continuously monitors the dark web, public code repositories and external sources for leaked credentials, API keys, tokens, secrets and other indicators of exposure. Every finding is reviewed by our analysts before it reaches your team, so you can focus on what truly requires action.
How Sentinel works
Years of combined senior security leadership
Assessments, audits and offensive engagements delivered
Proprietary products designed, built and maintained in-house
Exposure monitoring coverage for Sentinel clients
Tell us what you are trying to protect and what is in your way. A senior advisor will answer — not a sales team.