Home / Services / Salesforce Security
Service · PlatformSalesforce Security
Salesforce concentrates critical data, identities, integrations and business processes in one platform. We assess who and what can access it, then design the controls, Transaction Security policies and detection capabilities needed to protect it as the environment evolves.
Why it matters
Salesforce security is an access problem as much as a configuration problem.
Permissions accumulate, integrations gain broad scopes, service accounts outlive their original purpose and automation creates new paths to sensitive data. In a platform that evolves continuously, yesterday's secure configuration does not guarantee today's exposure.
We go beyond configuration review. Our Salesforce expertise allows us to design advanced, use-case-specific controls — from effective permission analysis and Transaction Security policies to modular IP filtering, Splunk-connected detections and custom safeguards for sensitive business processes.
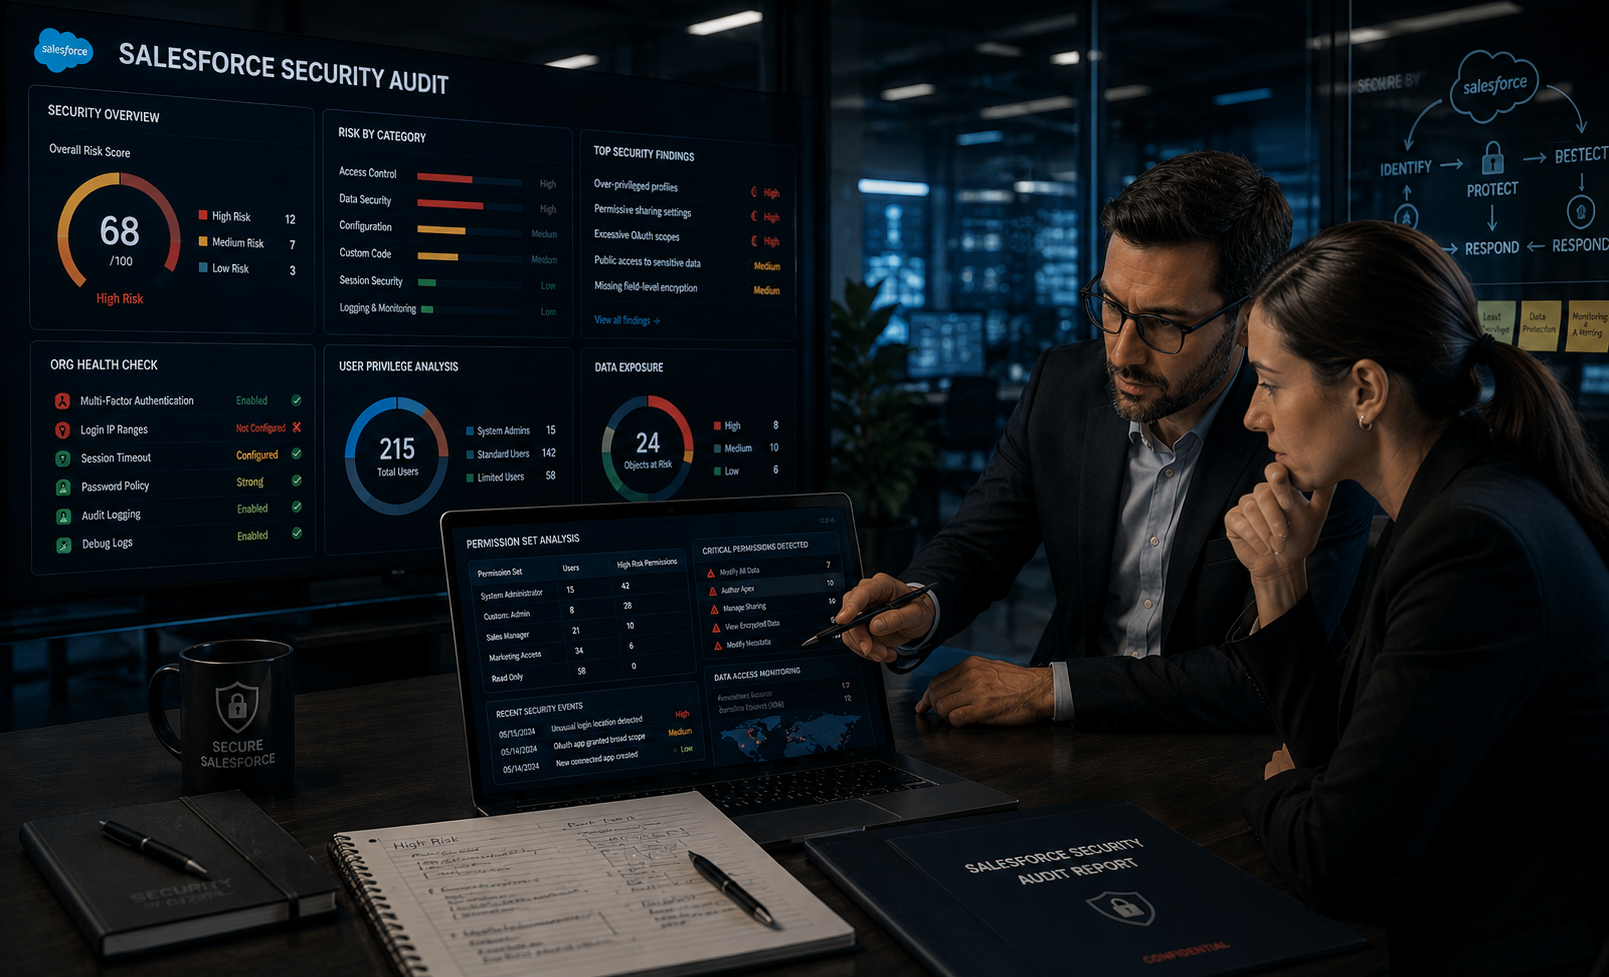
Assess the platform. Engineer the controls. Detect what matters.
Platform & Data Security
Organisation-wide settings, sharing architecture, data exposure and security controls protecting sensitive Salesforce data.
Identity & Permission Analysis
Profiles, permission sets, permission set groups, roles, sharing and effective access analysed to understand real permission scope and excessive privilege.
Transaction Security & Advanced Controls
Advanced Transaction Security policies and context-aware controls tailored to specific use cases, data flows, user populations and business risk.
Integrations, Code & Automation
Connected Apps, APIs, OAuth scopes, service accounts, Apex, Lightning and Flow reviewed for excessive trust, unsafe access paths and control gaps.
Monitoring & Detection Engineering
Salesforce event data connected to Splunk, with detection rules designed around privileged activity, anomalous access, exports, permission changes and other high-value scenarios.
From exposure analysis to engineered controls and detection.
Scaled to the environment — from focused permission reviews to advanced control and detection engineering programmes.
Assess the environment
Configuration, data model, sharing, identities, effective permissions, integrations, code and automation reviewed across the Salesforce environment.
Trace access paths
Effective permissions, Connected Apps, OAuth scopes and service accounts analysed to understand who — and what — can actually reach sensitive data and functionality.
Validate the exposure
Misconfigurations, excessive privileges and risky access paths are validated, then translated into Transaction Security policies, modular IP controls and other targeted safeguards.
Remediate & monitor
Controls are operationalised through monitoring and detection engineering — including Splunk integration and rules tailored to your highest-value Salesforce use cases.
What you receive.
Deliverables
- Full Salesforce security assessment across configuration, identity, data, integrations, code and automation
- Effective permission and sharing-scope analysis with least-privilege recommendations
- Advanced Transaction Security policies tailored to business-specific scenarios
- Modular IP filtering architecture for users, applications, environments and risk contexts
- Splunk integration design and Salesforce-specific detection rules
- Connected App, OAuth and service-account risk review
- Prioritised remediation and control-engineering roadmap
Ideal for
- Salesforce-first organisations holding regulated customer data
- Teams whose org has grown faster than its permission model
- Companies needing advanced Transaction Security, detection or access-control capabilities
- Organisations with complex integrations, service accounts, distributed teams or high-value Salesforce data
A Salesforce environment where access is understood, high-risk activity is controlled and detectable, and security rules are engineered around the way the business actually uses the platform.
Frequently combined with.
Build Salesforce controls around the risks that actually matter.
Tell us how Salesforce is used across your organisation, where the sensitive data sits and which use cases create the most risk. We will help analyse the access paths and engineer the right controls and detections.